Recovery after power outage in business
The power is back on, but that doesn't automatically mean operations are back to normal. A server might boot in the wrong order, a database could be out of sync, the network connection might be unstable, and employees may still lack access to key systems. Therefore, recovery after a power outage isn't just about switching on equipment. It's about confirming that data, systems, access, and security measures are working correctly before the company can rely on them again.
For small and medium-sized businesses, even a short power outage can have a greater impact than expected. Lost orders, a stalled service desk, inaccessible documents, and unclear customer communication can quickly add up. With clear responsibility, the right protection, and a tested response plan, the time it takes to get back to full capacity can be minimised.
What can go wrong when the power comes back on?
A power outage can be a localised problem in one office, but it can also affect network services, remote employees, and supplier systems. Although cloud services are usually still available, the company can still lose access if local network equipment, firewalls, or authentication services shut down.
The greatest risk often occurs during rebooting. If servers, storage, network devices, and workstations receive power at different times, connections can be lost, updates can get stuck, or data can be corrupted. An unexpected shutdown can also leave unfinished transactions in accounting, inventory, or business systems. The incident should be viewed as a potential security and data protection issue, not just a power disruption.
Power outages also create opportunities for fraud. When staff are under pressure to get back online, it's easier to click on false notifications about password resets, payment requests, or invitations to download a "fix". Restoration therefore needs to maintain the same security requirements as normal operations – sometimes even stricter.
The first few minutes are crucial
The first task isn't to get everyone back into all systems. The first task is to get an overview. The person in charge needs to confirm the extent of the disruption: Which locations were affected? Which systems shut down unexpectedly? Is the power stable, or is there a risk of another outage? Has any equipment shown warnings about temperature, battery, or disk errors?
Everything shouldn't be restarted at once. It's advisable to start with core systems in a defined order, for example, network connection and firewall, then authentication and storage services, and finally specialised operating systems. The order depends on the environment. A company relying on cloud services has different needs than a company with its own servers or on-site production equipment.
Staff must also be clearly informed during this time. Short messages about what is down, who is working on the issue, and when the next update is expected will reduce confusion and unnecessary service requests. If the company cannot respond to customers in the usual way, a pre-defined communication channel, such as a mobile phone, backup email address, or a notification in the relevant service channel, must also be activated.
Recovery after a power outage requires confirmation, not guesswork
Systems that appear to be operational may still have hidden faults. Therefore, systematic confirmation is required before staff are given the green light. This should cover the network, user accounts, backups, security measures, and critical business processes.
First, test whether employees can log in normally, both in the office and remotely if remote work is part of operations. Then, confirm that important files open, that printing and scanning work where relevant, and that key integrations between systems deliver correct information. It is not enough for the login page to appear. The business process itself must work from start to finish.
Security systems deserve special attention. Check the status of endpoint protection, whether device monitoring is active again, and if new alerts have appeared around the switch. If devices unexpectedly shut down, it is also necessary to check whether operating system or application updates have resulted in an unstable state. When in doubt about data quality, it is better to restore a verified copy than to continue with corrupted data.
Backups are only useful if they can be restored
Many companies take backups, but fewer test recovery regularly. This is a costly risk. Backups can fail silently, retention periods may be too short, or a critical system may simply not have been included in the backup policy.
A good plan defines which data and systems are most important, how much data loss the company can tolerate, and how quickly operations need to resume. These are business decisions, not just technical ones. Payroll systems, service desks, and sales systems, for example, may have vastly different recovery time requirements.
Backups must also be protected against the same events that affect the primary systems. If the only copy is in the same location, on the same network, or accessible with the same permissions, a power problem, failure, or network attack can affect both. Separate, monitored, and tested backups create a real safety net.
Backup power is part of the solution, not the entire solution
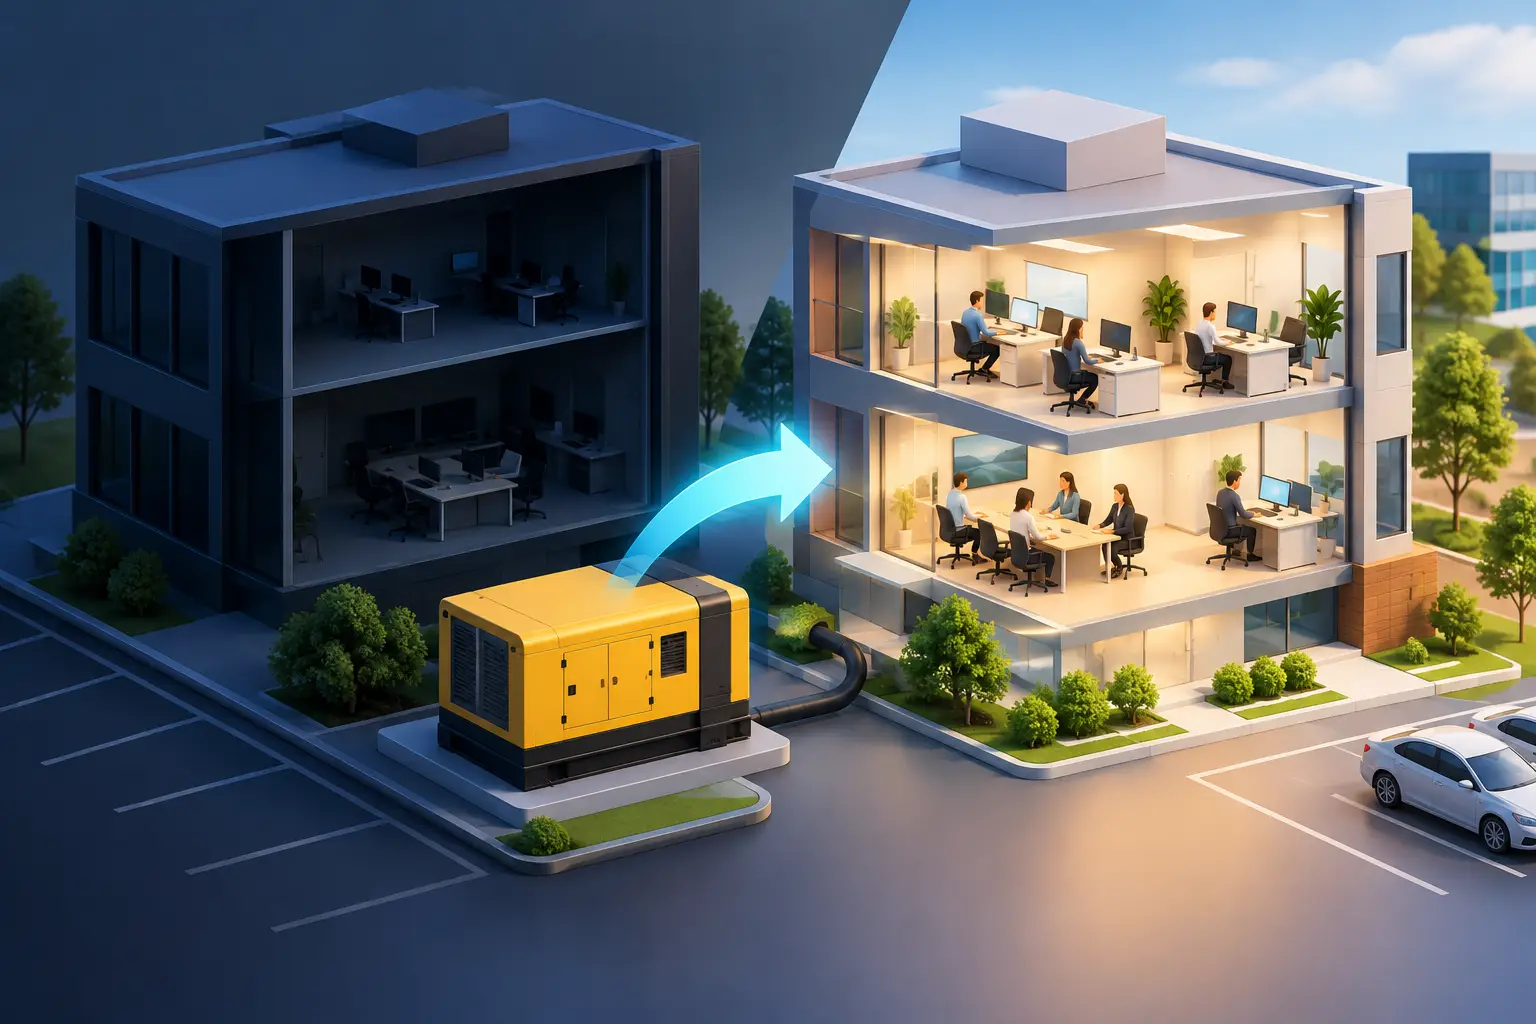
Battery systems and backup power can provide valuable time to shut down systems correctly or keep network connections running during a short outage. However, they are not a magic bullet. Batteries degrade, can be incorrectly sized, and generally cannot sustain full operation for long.
The correct setup depends on what needs to be protected. For some companies, it is important to keep the firewall, network switches, and internet connection running. For others, servers, storage, or telephone services need to be protected. With prioritization, you can protect what matters most to the operation, instead of blindly investing in backup power for the entire environment.
The equipment must be registered, tested, and monitored. If no one knows what devices are connected to backup power or how long they are expected to last, it is difficult to make the right decisions when the switch occurs.
The plan must specify people, not just technology
A response plan that only says "restart system" is of little help at seven in the morning when no one knows who is authorised to make decisions. It must mention responsibilities, contacts, the prioritisation system, and clear communication channels. It must also state when to stop and call for expert assistance.
Companies without a large in-house team especially need to know who takes ownership of the process. At nexIT, we work with clients to register the environment, monitor devices, protect endpoints, and build recovery plans that suit real operations. The goal is not to add complex tools, but to ensure that the right people can respond quickly and confidently.
Practice is just as important as documentation. Short, regular tests can reveal outdated phone numbers, missing authorisations, recovery that is too slow, or systems that no one had realised were important. Such tests cost time, but they usually cost much less than an unplanned shutdown in the middle of a busy day.
After the incident: fix the cause, not just the symptoms
When operations are stable, record what happened, what impact it had, and what delayed the recovery. Was the problem with electricity, equipment, settings, or a lack of clear responsibility? Were there security alerts that came too late? Did communication with staff and customers work?
This review should not be about finding a culprit. It should create actionable improvements: update contact lists, change the restart sequence, add monitoring, review backups, or secure important equipment with backup power. Small fixes after each incident can prevent major damage later.
Power outages cannot always be prevented. What a company controls is how well it is prepared, how quickly it regains oversight, and how reliably it trusts the systems again. A good recovery plan gives staff peace of mind, protects customer trust, and keeps the costs of disruptions in check when it matters most.