Traditional backup or cloud backup for businesses
Monday morning, staff cannot access the business system and the last backup turns out to be from a week ago. It then matters little whether the storage was cheap or the technology familiar. The question traditional backup or cloud backup is not primarily about where the data resides, but how quickly the company can resume normal operations.
For small and medium-sized businesses, lost emails, documents, financial data, or customer information can mean lost revenue, interrupted services, and damaged trust. Good backup is therefore operational protection. It must consider which data is important, how long the company can be offline, and what risks the operation can actually withstand.
Traditional backup or cloud backup: what is the difference?
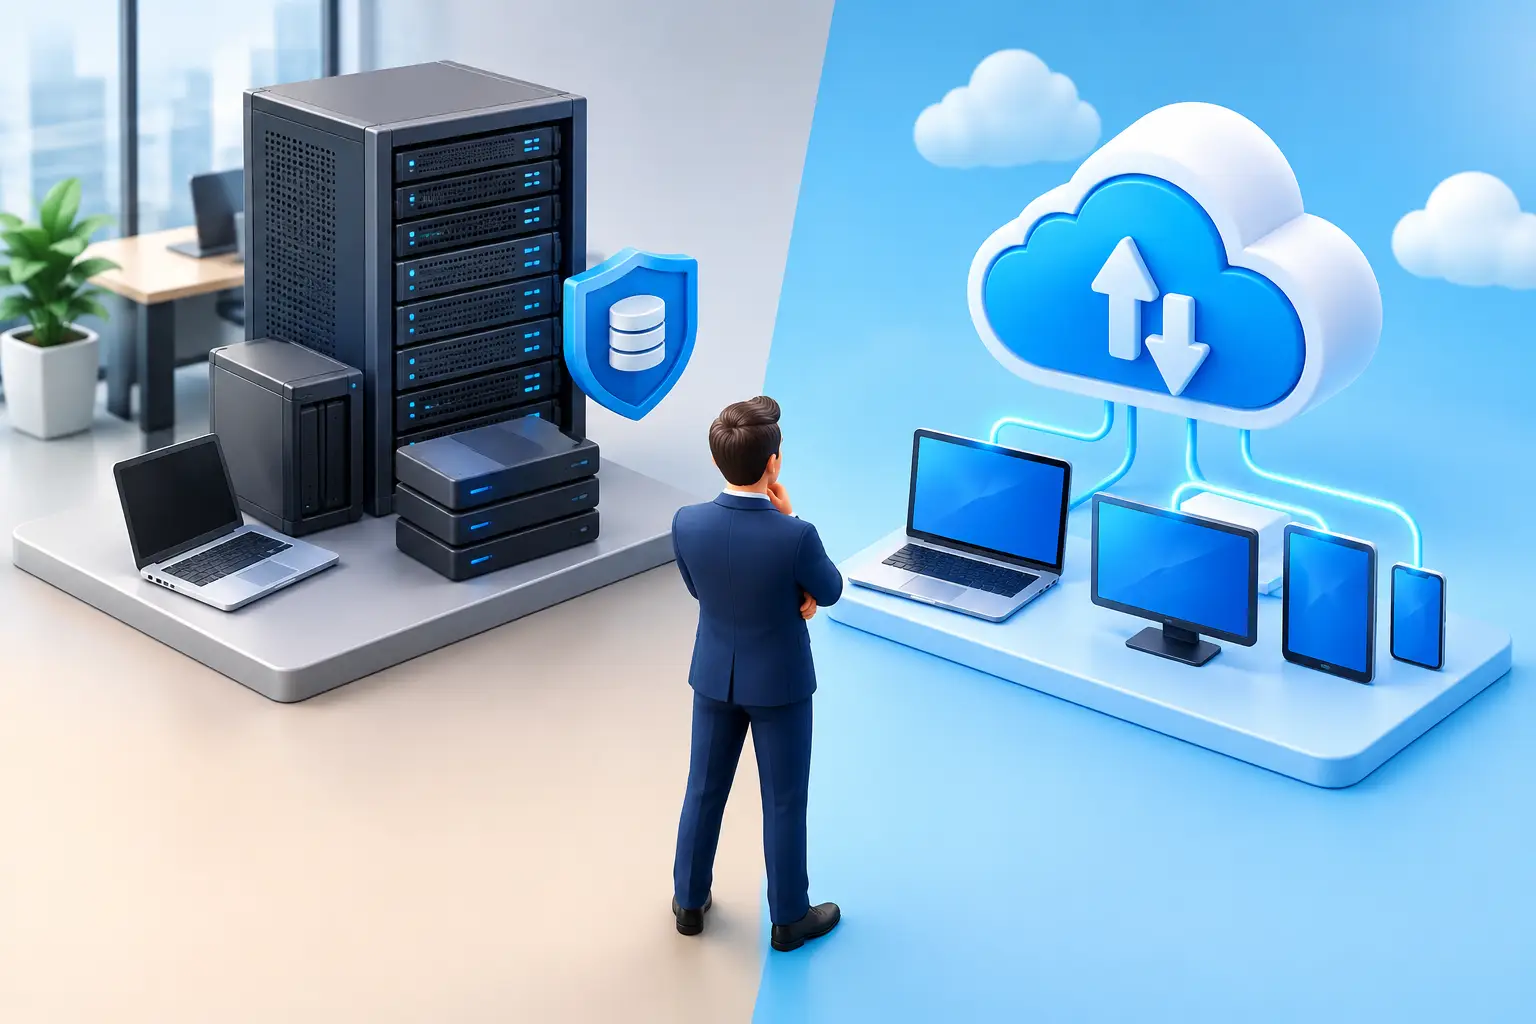
Traditional backup often means that data is backed up to local equipment, for example a server, NAS storage, external drive, or magnetic tape. The equipment is usually in the same building as the staff, sometimes in a locked IT cabinet or server room. The company then has direct control over the equipment and can often restore large datasets quickly over the internal network.
Cloud backup stores copies in a data centre operated by a service provider, separate from the company's premises. Backups are made over an internet connection according to a predefined schedule, and the data is usually encrypted both in transit and at rest. If a fire, water damage, burglary, or failure renders local equipment unusable, the backup is not at the same risk.
This is not a simple choice between old and new. Local backup can be very sensible when large amounts of data need to be restored quickly. Cloud backup, on the other hand, strengthens protection when an incident affects the entire site or when staff and equipment are dispersed. In most cases, the best solution is a combination of both methods.
Speed of recovery is often more important than the backup itself
A backup that has not been tested is not a confirmed recovery plan. This is one of the most common weaknesses we see in companies: backups appear to run normally, but no one has verified whether the data can be opened, a server rebuilt, or users returned to work within an acceptable timeframe.
Local backup can have an advantage when multiple terabytes need to be restored. If a server fails but the premises and internal network are intact, it can be much faster to retrieve data from local storage than to download it from the cloud. This is particularly true for companies working with large design files, videos, production data, or extensive datasets.
Cloud backup has another advantage. It allows a company to recover when local computer systems, office or storage equipment is unavailable. Some systems can also temporarily boot backed-up servers in a cloud environment. This can significantly shorten downtime, but requires that the service, internet connection and system prioritisation have been planned in advance.
The right question is therefore not just: "How often is a backup made?" It is also: "How long can we be without this system?" Email, accounting, sales systems, document storage and operating systems do not all have the same tolerance for downtime.
Set measurable recovery goals
Two concepts help managers make clear decisions. Recovery time describes how quickly a system needs to be back in operation. Data loss period, on the other hand, describes how much of the company's most recent data can be lost.
If a company can tolerate losing up to four hours of work, backups must be made at least every four hours. If the sales system cannot be down for more than one working day, the recovery plan must demonstrate, in practice and not just on paper, how this goal will be achieved.
These goals should differ depending on the system. It is rarely sensible to spend as much on recovery for an old document archive as for an active financial or service system.
Security risk: backups also become a target
Ransomware does not necessarily stop when a company's files are encrypted. Attackers often look for backups, delete them or try to encrypt them before demanding payment. A backup that is always connected to the same network, accessible with the same user accounts and unprotected against modification can therefore be a weaker defence than managers assume.
Local backups need to be protected against physical incidents and access misuse. An external drive in a drawer is better than no backup, but it helps little if it is in the same premises and the same backup process fails. There is also a risk that manual backups become irregular when workload increases or the responsible person is absent.
Cloud backup reduces the risk of local damage, but is not automatically secure. It is necessary to examine retention periods, access controls, multi-factor authentication, encryption and whether backups can be modified or deleted without special rights. Immutable backups, where data cannot be deleted or modified for a defined period, can be crucial after a cyberattack.
Good protection is based on a principle often called 3-2-1: having at least three copies of data, on two different storage media, and one copy off-site. In operations where cyberattacks are a real threat, it makes sense to add a backup that is protected against modification.
The cost is more than the price of storage space
Traditional backups may seem cost-effective initially. The company buys equipment and uses it for a few years. But the costs also include maintenance, disk replacement, monitoring, backup software, electricity, and staff time. If the equipment fails or runs out of space without warning, the savings can prove expensive.
Cloud backup is often paid for as a monthly service. This can lead to more predictable operating costs and reduce the need for your own storage equipment. On the other hand, costs and recovery times can increase as data volume grows, especially if large amounts of data need to be retrieved on short notice.
Therefore, it is important to compare the total costs, not just the monthly fee. What is the cost of one hour of downtime? What is the cost of losing the latest orders, payroll data, or customer communications? Once these questions are answered, it will be easier to see where investing in backups provides real operational security.
When is a hybrid solution best suited?
Most companies do not need to choose one approach exclusively. Local backups can ensure fast recovery for the most critical systems, while cloud backups can serve as an external safety net against major incidents. This reduces the likelihood that a single failure, misconfiguration, or attack will halt operations.
A hybrid solution is particularly suitable when companies have both cloud services and local systems. For example, Microsoft 365 is not the same as a dedicated backup process. Files, mailboxes, or users can be accidentally deleted, and retention settings are not necessarily designed to meet every company's recovery requirements. The same applies to document repositories and business systems hosted elsewhere.
At nexIT, we work with companies to define which data and systems need to be brought back online first. We then monitor backups, respond to errors, and test recoveries so that the plan is realistic when needed. The goal is not to add a complex system, but to make responsibility, cost, and protection clearer.
Questions to be answered before making a decision
Before choosing a backup solution, a company should be able to answer four questions: Which data will halt operations if lost? How recent does the recovered data need to be? How long can each key system be inaccessible? And who is responsible for monitoring errors and testing recoveries?
If the answers are unclear, it is not a sign that the company necessarily needs more expensive technology. It is a sign that the prioritisation needs to be mapped out first. A simple, well-managed solution with verified recoveries is better than a costly solution that no one owns or understands.
The next step does not have to be a major undertaking. Start with one critical system, verify when it was last successfully recovered, and then assess whether that result would keep operations running if a failure occurred tomorrow.