9 best ways to defend against ransomware
Last updated: 26 October 2026
Short Summary
You can protect yourself from ransomware by setting up multi-factor authentication, making backups using the 3-2-1 method, updating systems regularly, and training employees. These actions close vulnerabilities that attackers exploit to gain entry.
- Multi-factor authentication requires two or more confirmations and stops most attackers who steal passwords
- The 3-2-1 backup strategy means three copies on two media with one copy offsite
- The response plan should be printed and accessible without internet to use during the first 60 minutes of an attack
- Employees are the first line of defence and require monthly training on phishing and security rules
Table of Contents
- What is ransomware and how big is the threat?
- Preliminary precautions: Identifying threats and vulnerabilities
- Multi-factor authentication as the first line of defence
- Company backups as recovery against attacks
- The 3-2-1 backup strategy for reliable data storage
- Cyber attack response and recovery plan
- Staff training and adaptation to security rules
- Consultation with professionals to strengthen defence
- Frequently Asked Questions
What is ransomware and how big is the threat?
Ransomware is malicious software that locks your data and demands payment to unlock it. Attackers use it to halt company operations and force owners to pay large sums. For small and medium-sized businesses, a single attack can mean operations stop completely for days or weeks.
The threat is not theoretical. Companies you know are put in this situation regularly. When ransomware strikes, employees cannot access their documents, customers get no response, and revenue disappears. Many company managers simply pay to regain access, but this does not guarantee the data will be returned and it encourages attackers to continue.
What most companies miss is that ransomware doesn't come from nowhere. It enters your systems through vulnerabilities that could have been closed. We help companies defend against ransomware by closing these holes before attackers find them.
Here are nine of the best ways to defend against ransomware and ensure your business keeps running.
Preliminary precautions: Identifying threats and vulnerabilities
You cannot protect what you cannot see. The first step is to know where your data is, how people access it, and which systems are actually in use. Many administrators think they know this, but when it comes to an actual audit, the list turns out to be incomplete.
Start with three simple questions:
- What devices are on your network? Laptops, phones, printers, industrial computers, cameras, and even coffee machines can be on the same network. Every device is a potential entry point.
- Who has access to what data? Employees, contractors, service providers, and former employees. Access that was necessary last year can be an unnecessary risk today.
- What software is in use and when was it last updated? Operating systems, browsers, Office suites, and specialised applications. Updates close known vulnerabilities that attackers exploit.
Record the answers in a simple spreadsheet. You don’t need expensive software to start. The most important thing is that the record exists and someone is responsible for keeping it updated.
After you have mapped the situation, prioritise. Don’t try to fix everything at once. Start with what is easy, cheap, and has the biggest impact: updates, strong passwords, and multi-factor authentication. More complex tasks, such as network segmentation and monitoring, can be moved to a later phase.
Get a successful small business security audit to get an external assessment of the situation. Professionals can see vulnerabilities you might not see yourself, such as open ports, old services, or incorrect access permissions. The audit should deliver a report with prioritised actions, not just a list of problems.
Don’t let the audit end up as a document in a drawer. Set a specific date for each action and one responsible person. Otherwise, nothing will get done.
Finally: repeat the assessment regularly, at least annually or when there is a change in operations, such as new employees, new systems, or a move to the cloud. The threat changes, and your defence must keep up.
Multi-factor authentication as the first line of defence
Most attackers gain access by stealing passwords. They can do this through phishing, by buying stolen passwords online, or by guessing weak passwords.
Multi-factor authentication (MFA) requires two or more confirmations before someone can log in. Even if an attacker has the password, they cannot get in without the second factor, usually a code on your mobile phone or a biometric confirmation.
This stops most attackers. They want easy targets, not systems that are difficult to break.
Put MFA on everything that matters:
- Employee email accounts
- Database access accounts
- System administrator accounts
- Document repositories and cloud systems
Are you still relying on SMS as an MFA solution? SMS is better than nothing, but it is no longer considered sufficiently secure. Use app-based authentication or security keys where possible.
Company backups as recovery against attacks
Ransomware works by making data inaccessible. But if you have a backup that the attacker cannot reach, you can endlessly restore everything without paying.
Business backups are copies of your data stored in a secure location and separate from your main system. When an attack occurs, you can restore your data from the backup.
The problem is that many administrators create backups that are not separate. They copy data to the cloud that is connected to the same network. Attackers can often delete these backups too.
Backups must be:
- Stored off your main system
- Immutable (an attacker cannot delete older versions)
- Tested regularly to ensure they work
We help companies set up business backups that are separate and secure. Learn how Acronis Cyber Protect for growing businesses combines backup, protection, and recovery.
The 3-2-1 backup strategy for reliable data storage
This is the strategy that professionals use. It is simple and it works.
The 3-2-1 backup strategy means: three copies of your data, on two different types of media, with one copy offsite.
It breaks down like this:
- 3 copies: your main system + two backups
- 2 media: e.g. hard drive + cloud
- 1 offsite: at least one copy in another location (not the same building)
Example: Your data is on a server. You back it up to an external hard drive. You also back it up to the cloud with a trusted provider. Now an attacker has three targets to break instead of one.
This strategy doesn't cost much more than bad backups. It doesn't take longer. But it changes whether you can recover data after an attack.
Implement the 3-2-1 backup strategy now. Not next month. Now.
Professionals use this simple strategy to ensure data is always recoverable.
| Factor | Meaning | Example |
|---|---|---|
| 3 copies | Main system + two backups | Server + external drive + cloud |
| 2 media | Different types of storage | Hard drive and cloud |
| 1 offsite | Copy in another location | Cloud with a trusted provider |
Cyber attack response and recovery plan
Even if you do everything right, an attack can still happen. What matters most is what you do in the first few hours. Companies without a plan lose valuable time in chaos; companies with a plan know who does what and when.
A disaster recovery plan is not a document to be left in a drawer. It should be printed, accessible without the internet, and tested regularly.
First 60 minutes:
- Isolate the infected systems. Take them offline, but do not shut them down immediately unless instructed to do so. Shutting down can destroy evidence and make recovery more difficult.
- Notify internally. Inform management, IT staff, and legal counsel. Do not try to resolve the issue in secret.
- Record everything. What was seen, when, what messages appeared, what devices were infected. This is necessary for further investigation and recovery.
- Contact professionals. If you do not have an in-house IT team, call your service provider or a specialised response team.
Notification to authorities:
In Iceland, it is important to know your obligations. If personal data is involved, there may be a duty to notify. Seek advice from the Data Protection Authority (Persónuvernd) and follow their guidelines on notification of a security breach. You can also seek assistance from CERT-Iceland, which provides advice and support for responding to cyber attacks (RFC-2350). Contact them at the beginning of the incident, not after the damage has occurred.
Do not pay a ransom. Payment does not guarantee the return of data and encourages attackers to continue. Some attackers sell the data they have obtained even if payment is made.
Recovery:
- Use backups that are separate from the main system. If you have 3-2-1 backups, you can restore from a backup that the attacker could not access.
- Restore in the correct order: first the operating system and basic services, then data, and finally user access.
- Test the recovery in an isolated environment before putting the systems back into operation.
- Record what succeeded and what failed. This will be the basis for an improved plan.
Learn how to create a business continuity plan that protects operations, data, and staff when a cyber attack suddenly halts operations.
After the attack:
Review what went wrong and update your defences. It often turns out that the same entry point could have been blocked with a simple update or better access control. Assess what lessons can be learned and change processes to prevent the same attack from happening again.
Keep the response plan on paper and in a secure offline location. If the network is down, you cannot open a document stored on an infected system.
Staff training and adaptation to security rules
Most attackers get in because an employee clicks on a bad link or gives up their password.
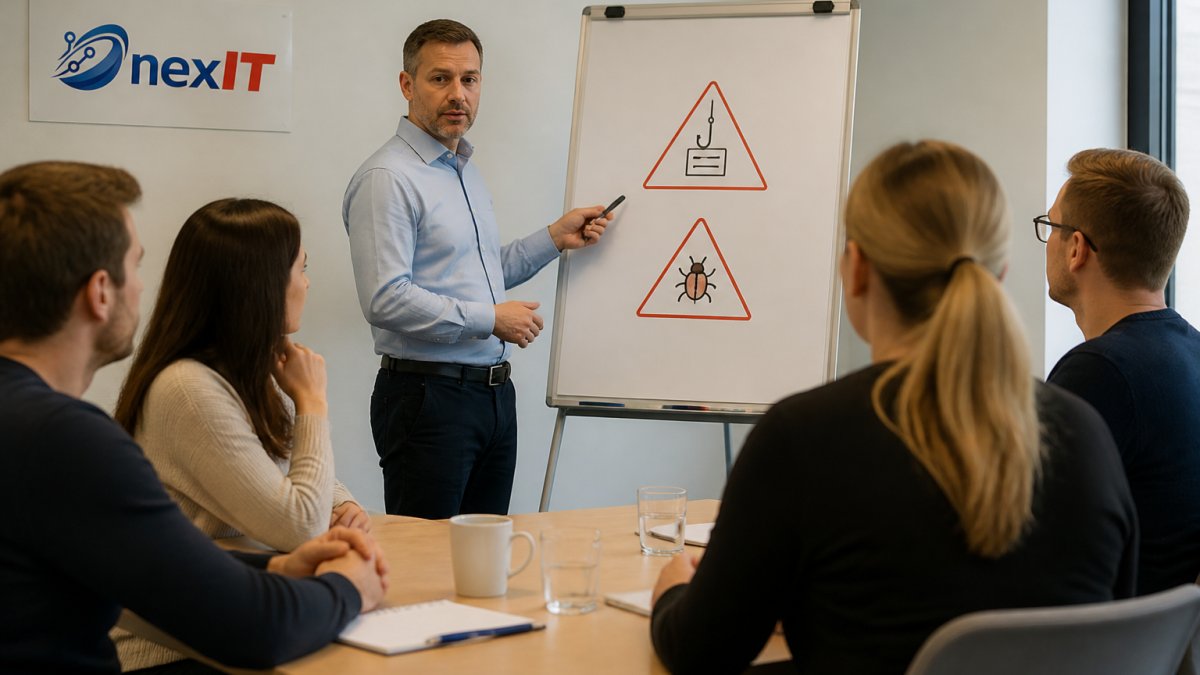
This is not because employees are stupid. It is because they do not know what to look for. Phishing emails look like real emails. Malicious software can be hidden in content that appears trustworthy.
Your employees are your first line of defence. They need to know:
- How to identify phishing
- What to do if they see suspicious emails
- How to use strong passwords
- Why MFA matters
Learn how to train staff against phishing with regular exercises, clear responses, and measurable results that significantly reduce the company's risk.
Training should happen regularly, not just once a year. Monthly drills and short announcements keep security top of mind for people. Companies that train their employees regularly see fewer attacks.
Consultation with professionals to strengthen defence
You could try to do all of this yourself. But cybersecurity is complex and it changes rapidly. What was secure last year might be weak today.
Professionals see attacks on many companies. They know what works and what doesn't. They know how attackers think. They can set up systems that are hard to break and easy to use.
We help companies defend against ransomware with a comprehensive approach. We set up MFA, backups, response plans, and training. We monitor your systems and we change them when new threats emerge. We are here if an attack happens.
Consulting with professionals is not expensive. It is cheaper than paying ransoms or recovering after an attack. It is cheaper than losing customers because your systems are down.
Ransomware is not an example of what could happen. It is an example of what does happen. But you can protect your company. Start by knowing your weaknesses. Put MFA in place. Back up your data with the 3-2-1 method. Prepare yourself with a response plan. Train your employees. And contact professionals to strengthen your defence. Contact nexIT and we will help you set all this up so you can focus on what matters to your company.
Frequently Asked Questions
What is ransomware and how does it get into a company's computer system?
Ransomware is malicious software that encrypts a company's data, making it inaccessible until payment is made. It often enters through fraudulent emails, insecure websites, unpatched systems, or through employees clicking on malicious links. Companies not prepared with backups and a response plan face a greater risk of damage and cost.
How does multi-factor authentication help defend against ransomware?
Multi-factor authentication requires users to verify themselves with more than one method, e.g. a password and a verification code on a phone. Even if malicious actors obtain an employee's password, they cannot access the system without a second verification. This prevents unauthorised access and greatly reduces the risk of a ransomware attack or unauthorised access.
How often should a company back up its data?
Most companies should perform daily or weekly backups, depending on how critical the data is and how often it changes. Healthcare facilities and companies with sensitive data should consider daily backups. It is important to ensure that backups are stored offline and that they are tested regularly to ensure data can be recovered if a ransomware attack occurs.
Should a company pay a ransom after a cyberattack?
Most experts recommend not paying ransoms. Payment does not guarantee data recovery and finances malicious actors to continue attacks. Instead, a company should rely on its backups, report to authorities if necessary, and work with professionals on recovery. With a good response plan and security backups, companies can get through attacks without paying malicious actors.